Cybersecurity Incident Response System
Create A Clear Response Process Before A Cybersecurity Incident Disrupts The Business
A cybersecurity incident can begin with something small. An employee account behaves strangely. A website starts receiving unusual traffic. A device shows signs of malware. Customer information may have been exposed. Files suddenly become inaccessible.
The technical problem matters, but the business response matters too. Without a defined process, employees may not know who should investigate, which systems should be isolated, what information should be preserved, who has authority to make decisions or when outside assistance should be contacted.
The Cybersecurity Incident Response System creates a repeatable process for identifying a suspected incident, assessing what happened, containing affected systems, coordinating the response and restoring normal operations.
Its purpose is not to automate every cybersecurity decision. It gives the business an organized response structure so technical specialists and business leaders can act from shared information instead of improvising during an incident.
NIST’s current guidance reflects this broader approach. Incident response should be incorporated throughout cybersecurity risk management rather than treated as an isolated technical procedure. (NIST Computer Security Resource Center)
Which Stax Fits Your Business
| Business Need | Stax | Software | Cost |
|---|---|---|---|
| Website focused protection, visibility and response controls | Starter Stax | Cloudflare | Free and paid plans |
| Centralized security monitoring and incident investigation across business systems | Growth Stax | Wazuh | Open source with cloud options available |
| Managed detection and response for businesses needing outside security expertise | Pro Stax | Huntress | Varies by environment and service |
Pricing and capabilities change over time and should be confirmed directly with each provider before purchase.
Software Linx
Starter
Growth
Pro
Blueprint Overview
| Metric | Value |
|---|---|
| Category | Cybersecurity |
| Business Problem | Security incidents can become larger while staff determine how to respond |
| Primary Objective | Create a defined process for detecting, assessing, containing and recovering from cybersecurity incidents |
| Core Signals | Security alerts, unusual account activity, malware, suspicious network activity, system changes and user reports |
| Setup Time | Approximately 2 to 4 hours for the initial response framework |
| Difficulty | Intermediate |
| Maintenance | Periodic testing and revision |
| Best For | Small businesses that depend on websites, cloud services, employee accounts, customer data or connected devices |
| Primary Output | Incident status, assigned response actions and recovery process |
The Hidden Operational Leak
| Without This Blueprint | With This Blueprint |
|---|---|
| Employees react independently to suspicious activity | A defined response process establishes responsibilities |
| Security alerts may remain disconnected | Relevant information can be gathered into an incident record |
| Staff may not know what should be isolated | Containment responsibilities are established beforehand |
| Evidence can disappear during hurried troubleshooting | Relevant information can be preserved during response |
| Business leaders receive incomplete information | Incident status can be communicated through a defined process |
| Recovery begins without confirming the incident is contained | Containment and recovery become separate decisions |
| The business returns to normal without reviewing what happened | Lessons can improve future security controls |
Modern incident response is not simply about cleaning an infected computer. NIST notes that incidents have become broader and more complex and that recovery can sometimes take weeks or months. Continuous improvement is therefore part of the current incident response model. (NIST Computer Security Resource Center)
Business Impact Snapshot
| Area | Potential Impact |
|---|---|
| Response Time | Staff know where an incident should be reported and who should respond |
| Containment | Affected systems can be evaluated before the incident spreads further |
| Coordination | Technical and business responsibilities become clearer |
| Recovery | Restoration follows an organized process |
| Documentation | Decisions and incident information remain available for later review |
| Resilience | Lessons from incidents can improve future security controls |
Real World Example
A small professional services company uses cloud email, shared files, several employee laptops and an online customer portal.
One employee reports that their email account is behaving strangely.
Shortly afterward, another employee receives an unexpected message apparently sent from the first employee’s account.
Nobody yet knows whether the account has actually been compromised.
Without an incident response process, employees begin investigating independently. Someone changes a password. Another employee deletes suspicious messages. Management contacts the website administrator even though the website may not be involved.
The Cybersecurity Incident Response System creates a different sequence.
The suspicious activity is recorded as a potential incident. The affected account is identified. The assigned responder reviews available evidence and determines what other accounts or systems may be involved.
Access can be restricted where appropriate while the investigation continues.
The business documents what happened, restores affected services when it is reasonable to do so and reviews the incident afterward.
The value of the system is not predicting every possible cyberattack. It is giving the business a response structure when something unusual actually happens.
WIZESTAX Stax Options
Starter Stax
Cloudflare
Best For
Small businesses whose primary internet exposure is a website, ecommerce property, application or other public facing online service.
| Function | Software |
|---|---|
| Website Security | Cloudflare |
| Traffic Monitoring | Cloudflare |
| Application Protection | Web Application Firewall |
| Threat Blocking | Cloudflare Security |
| Security Visibility | Security Center |
| Response Controls | Cloudflare Dashboard |
Advantages
| Benefit |
|---|
| Strong fit for internet facing websites and applications |
| Security controls can block malicious web requests |
| Traffic information can help investigate abnormal activity |
| Security Center can identify configuration risks and vulnerabilities |
| Small business plans are available |
| Security and website performance can operate through the same platform |
Limitations
| Limitation |
|---|
| Does not replace security monitoring across employee devices and every business system |
| Primarily protects infrastructure routed through or integrated with Cloudflare |
| Security configuration still requires knowledgeable decisions |
| A broader incident may require additional tools and outside expertise |
Cloudflare currently positions its small business platform around website and application protection, including its Web Application Firewall. Its Security Center can also identify security risks, misconfigurations and vulnerabilities across connected domains. (Cloudflare)
Growth Stax
Wazuh
Best For
Businesses with technical support that want broader monitoring across endpoints, servers, cloud workloads and security events.
| Function | Software |
|---|---|
| Endpoint Monitoring | Wazuh |
| Security Events | Wazuh |
| Threat Detection | Wazuh |
| Log Analysis | Wazuh |
| File Integrity Monitoring | Wazuh |
| Incident Investigation | Wazuh Dashboard |
Advantages
| Benefit |
|---|
| Open source security platform |
| Broader visibility than website only protection |
| Endpoint and server activity can contribute to investigation |
| Centralized security events support incident analysis |
| Can support businesses operating mixed technology environments |
Limitations
| Limitation |
|---|
| Requires more technical knowledge |
| Alerts still need human investigation |
| Deployment and tuning can require significant work |
| Small businesses without internal technical support may find the platform difficult to operate |
Pro Stax
Huntress
Best For
Businesses that want security monitoring supported by outside specialists rather than building a complete internal security operation.
| Function | Software |
|---|---|
| Managed Detection | Huntress |
| Endpoint Security | Huntress |
| Identity Monitoring | Huntress |
| Security Investigation | Huntress Security Operations |
| Incident Escalation | Huntress |
| Response Support | Managed Security Team |
Advantages
| Benefit |
|---|
| Managed security model reduces dependence on an internal security team |
| Human security specialists can investigate suspicious activity |
| Endpoint and identity risks can be monitored |
| Security findings can be escalated for action |
| Appropriate for businesses that cannot maintain a dedicated security operations function |
Limitations
| Limitation |
|---|
| Higher operating cost than self managed security tools |
| Coverage depends on the services deployed |
| Businesses still need internal decision makers during incidents |
| Managed detection does not eliminate the need for backups, policies and recovery planning |
How The Three Stax Differ
| Stax | Primary Approach |
|---|---|
| Cloudflare | Internet facing website and application protection |
| Wazuh | Self managed centralized security monitoring |
| Huntress | Managed detection and response |
These are different implementation architectures rather than rankings.
A small business primarily concerned with its public website has a different security environment from a company operating dozens of employee devices and servers. A business without internal security expertise may need a managed architecture rather than another monitoring dashboard.
Copy And Paste Internal Incident Alert
“Potential cybersecurity incident reported at {{time}} involving {{system_or_account}}. Do not make unrelated changes to the affected system until the incident has been reviewed. Record any unusual activity you observed and send it to {{incident_owner}}.”
Copy And Paste Employee Security Notice
“We are investigating a security issue involving {{affected_service}}. Please follow the temporary instructions provided by the response team. Do not delete suspicious messages, install software or make security changes unless instructed. Report any related unusual activity immediately.”
Copy And Paste AI Prompt
You are assisting a small business with cybersecurity incident documentation.
Review the incident information provided and organize the known facts.
Separate confirmed information from suspected activity.
Identify affected accounts, devices, applications and business services when that information is available.
Create a timeline using only the information provided.
Identify information that still needs investigation.
Do not assume that suspicious activity confirms a security breach.
Do not invent attackers, malware, vulnerabilities, affected systems or data exposure.
Do not recommend destroying files, logs or other potential evidence.
Clearly identify decisions that require a qualified cybersecurity professional.
If the available information is insufficient to determine the scope of the incident, state that further investigation is required.
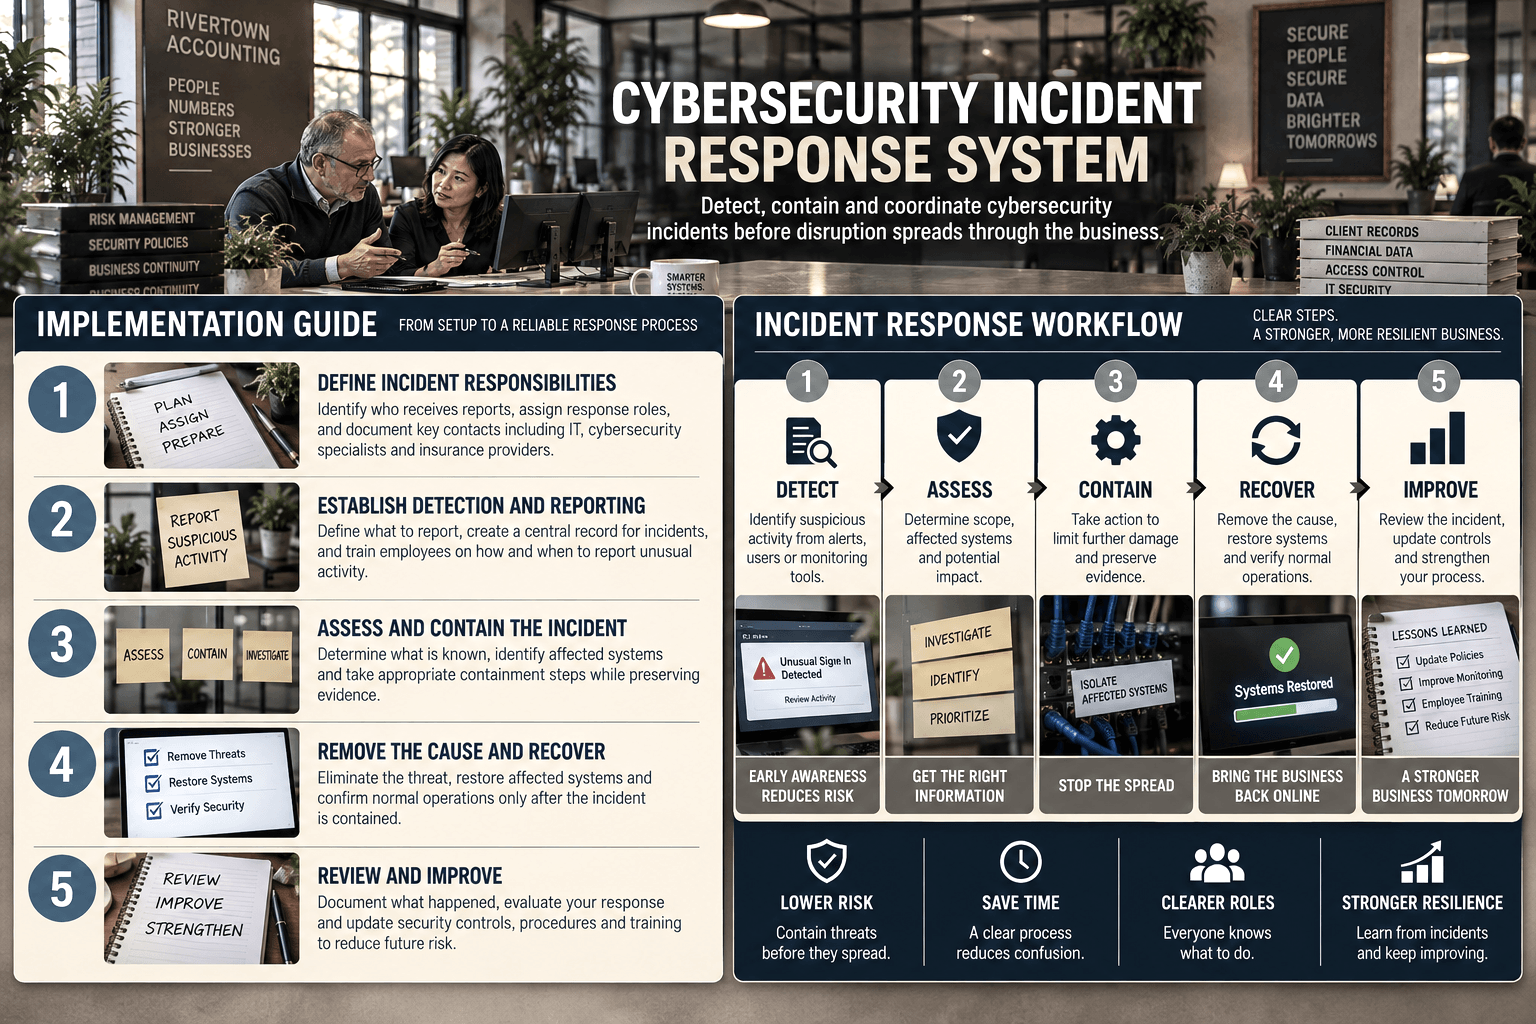
Step By Step Implementation Guide
The following setup demonstrates one vendor neutral implementation path based on current NIST incident response guidance.
It is not a WIZESTAX recommendation for a particular security product.
NIST is used here because SP 800 61 Revision 3 provides a current vendor neutral framework for integrating incident response into cybersecurity risk management. (NIST)
Step 1: Define Incident Responsibilities
Identify who receives reports of suspicious activity.
Assign the person responsible for coordinating the initial response.
Record contact information for outside technology providers, cybersecurity specialists, insurance contacts and other relevant resources.
Determine which business leaders have authority to make decisions involving system shutdowns, customer communication and operational disruption.
Employees should know where to report suspicious activity before an incident occurs.
NIST Incident Response Resources
Step 2: Establish Detection And Reporting
Define the types of events employees and security systems should report.
Examples include unusual account activity, malware warnings, unexpected password resets, suspicious messages, unexplained system changes and security alerts.
Create one location for recording incidents.
Record when the activity was discovered, who reported it, what systems may be involved and what evidence currently exists.
A report begins an investigation. It does not automatically prove that a security breach occurred.
Step 3: Assess And Contain The Incident
Determine what is actually known.
Identify potentially affected accounts, devices, applications and services.
Qualified personnel should determine appropriate containment actions based on the incident.
Containment can involve restricting compromised accounts, isolating affected devices or blocking malicious activity, but the correct action depends on the situation.
Preserve relevant information whenever possible.
Current CISA response procedures similarly emphasize containment before eradication and preservation of evidence when appropriate. (CISA)
Step 4: Remove The Cause And Recover
Once the incident has been sufficiently understood and contained, determine what must be corrected before normal operation resumes.
This may involve removing malicious software, correcting compromised credentials, fixing vulnerable systems, restoring clean data or rebuilding affected devices.
Recovery should be deliberate.
Systems should not simply be returned to normal because the immediate symptoms have disappeared.
CISA’s response playbook describes eradication and recovery activities that can include removing incident artifacts, rebuilding from clean sources and checking that malicious code has been removed. (CISA)
Step 5: Review And Improve
Document what happened.
Review how the incident was detected.
Identify which controls worked and which did not.
Determine whether employees had the information and authority they needed.
Update security controls, procedures and training where appropriate.
NIST’s current model explicitly incorporates continuous improvement so lessons identified during response can strengthen future cybersecurity risk management. (NIST Computer Security Resource Center)
Incident Exposure Snapshot
The economic value of incident response depends heavily on the system affected and the severity of the event.
| Incident Area | Possible Business Exposure |
|---|---|
| Employee Account | Unauthorized access and fraudulent communication |
| Customer Data | Privacy, contractual and reputation consequences |
| Business Email | Impersonation and payment fraud |
| Website | Lost availability and customer access |
| Business Files | Operational interruption and possible data loss |
| Payment Systems | Transaction disruption |
| Employee Devices | Malware spread and lost productivity |
These are potential areas of exposure rather than predictions of loss. Actual consequences depend on the incident, affected systems, data involved, contractual obligations and applicable law.
WIZESTAX Diagnostic Scorecard
| Category | Assessment |
|---|---|
| Economic Problem | Security incidents can grow while the business determines how to respond |
| Signal Quality Required | High |
| Automation Potential | Moderate |
| Human Judgment Required | Very High |
| Data Dependency | High |
| Scalability | High |
| Primary Value | Faster coordinated incident response |
| Primary Risk | Acting on incomplete or incorrectly interpreted security information |
Common Mistakes
| Mistake | Result |
|---|---|
| Waiting for an incident before assigning responsibilities | Staff improvise during a time sensitive event |
| Treating every alert as a confirmed breach | Resources are wasted and unnecessary disruption can occur |
| Ignoring employee reports because automated tools show nothing | Important human observations can be missed |
| Deleting suspicious files or messages immediately | Potential evidence can disappear |
| Restoring systems before understanding the incident | The underlying problem may remain |
| Allowing everyone to make independent security changes | Investigation becomes harder to coordinate |
| Keeping no incident timeline | Important decisions and events become difficult to reconstruct |
| Never reviewing completed incidents | The same weaknesses can remain in place |
Related WIZESTAX Categories
| Category | Related Business Problem |
|---|---|
| Operations | Business Document Expiration |
| Human Resources | Employee Access Removal |
| Operations | Operational Exception Dashboard |
| Operations | Business KPI Anomaly Alert |
| Vendors | Vendor Document Collection |
| Vendors | Vendor Insurance Expiration |
These remain separate problems. Cybersecurity Incident Response System owns the operational response to a suspected or confirmed cybersecurity event. Employee Access Removal controls access when a worker leaves. Business Document Expiration prevents organizational records from quietly lapsing. Operational Exception Dashboard identifies broader operational abnormalities rather than cybersecurity incidents.
Get New WIZESTAX Blueprints Every Monday
Subscribe to receive new WIZESTAX Blueprints covering Customer Retention, Marketing, Sales, Finance and Operations directly to your inbox.